SICHERTEN works with regulated enterprises and fast-moving product companies in India and around the world. From RBI-regulated banks and ABDM health platforms at home to SaaS, fintech and financial firms across the Middle East, the United States and Australia, we deliver the security and privacy assurance your regulators and customers expect, against Indian rules and international standards alike.
Client references available on request.
We’re happy to connect you with organisations we’ve worked with in your sector or region.
From our base in Hyderabad, we serve organisations across India, the Middle East, the United States and Australia.
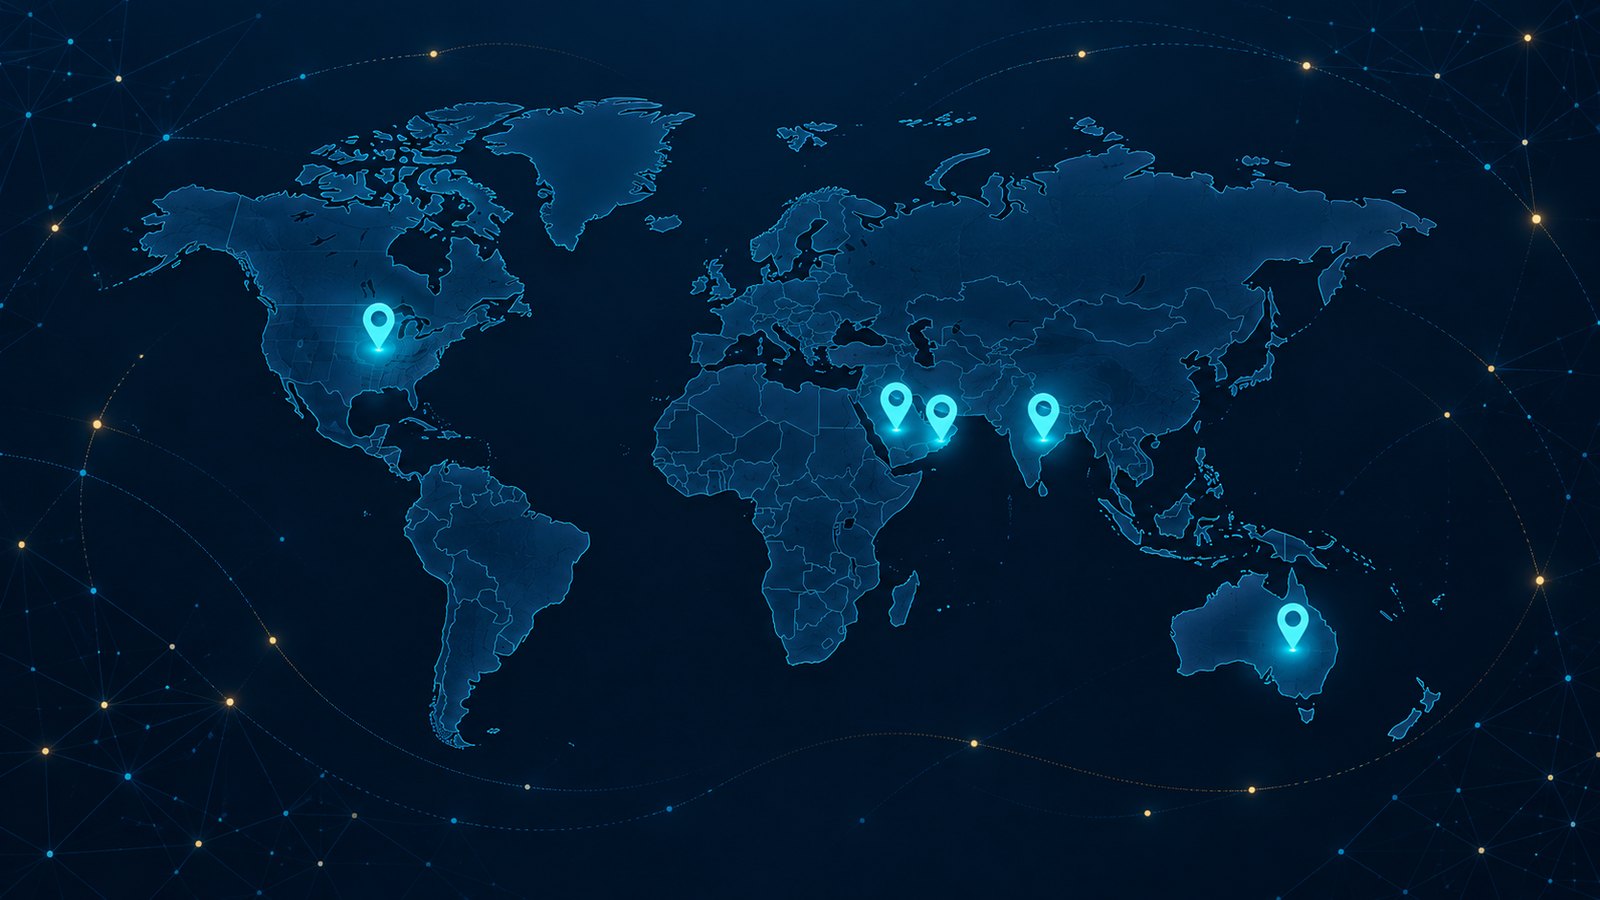
Whether your obligation sits with a European regulator, a US customer’s security review, a Gulf data-protection authority, an Australian requirement or India’s own regime, we work to the standard that applies to you.
Wherever sensitive data, regulatory scrutiny or customer trust is on the line, we help teams prove their security.
Banks, NBFCs, insurers and payment firms come to us for mandated audits, RBI IS audits, SEBI CSCRF, IRDAI, NPCI, CICRA and ABDM/WASA, delivered by a CERT-In empanelled team that speaks the regulator’s language.
SaaS and technology companies rely on us for penetration testing, application security and embedded security testing inside their SDLC, so they can ship fast without shipping risk.
Organisations pursuing SOC 2, ISO 27001 or ISO 42001 use our readiness and implementation support to reach attestation with confidence and without surprises.
Startups and scale-ups get right-sized guidance and vCISO support, building a security and compliance foundation that scales with them rather than slowing them down.
Tell us about your organisation and what you need to assure, we’ll take it from there.